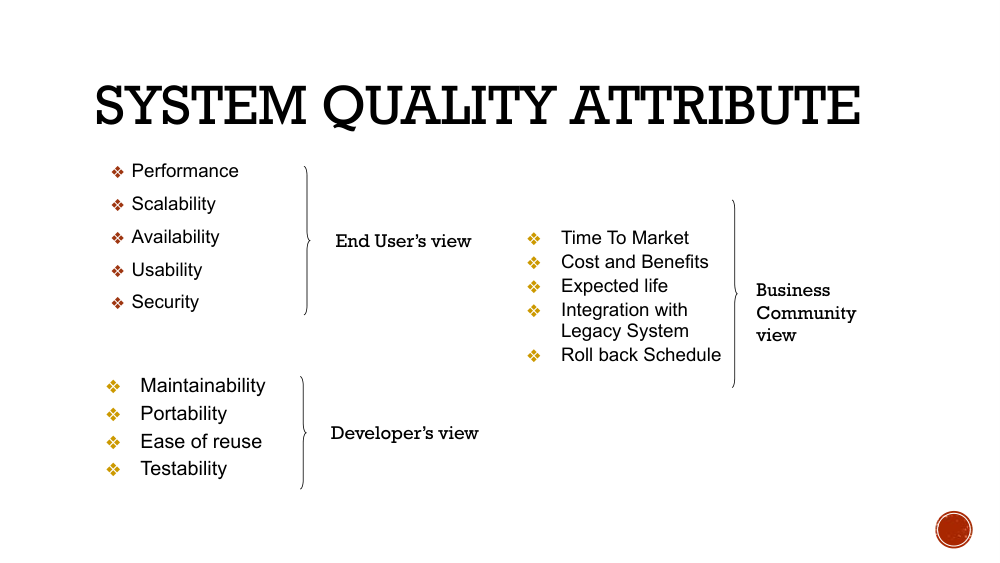
The Architecture Tradeoff Analysis Method (ATAM) is a structured approach to evaluating software architecture before expensive implementation choices become difficult to reverse. Rather than asking only whether the system delivers required functions, ATAM asks whether the architecture is likely to support the qualities stakeholders care about: performance, scalability, availability, security, usability, maintainability, portability, testability, time to market, cost, and other business concerns.
Key takeaways
- ATAM evaluates architectural decisions in the context of prioritized quality-attribute requirements.
- The method connects business drivers to concrete scenarios and then to architectural approaches.
- Its most useful outputs are architectural risks, non-risks, sensitivity points, tradeoff points, and risk themes.
- ATAM is a risk-identification and architecture-evaluation method: not a substitute for detailed performance testing, security assessment, or functional verification.
- The process improves communication because stakeholders make assumptions, priorities, and decision rationale explicit.
What is the Architecture Tradeoff Analysis Method?
ATAM was developed at Carnegie Mellon University’s Software Engineering Institute (SEI) as a method for evaluating a software architecture relative to its quality-attribute goals. The core idea is straightforward: software architecture is rarely “good” in the abstract. It is good or unsuitable relative to specific goals, constraints, workloads, users, threats, operating conditions, and business priorities.
That is why ATAM analyzes decisions in context. A caching layer might improve response time but complicate consistency. Replication may improve availability while increasing operational complexity and cost. Stronger security controls can change latency or usability. A highly modular architecture may improve modifiability but introduce more network calls, deployment units, and failure modes. ATAM helps a team make these interactions visible before they turn into production surprises.
Why architecture needs early analysis
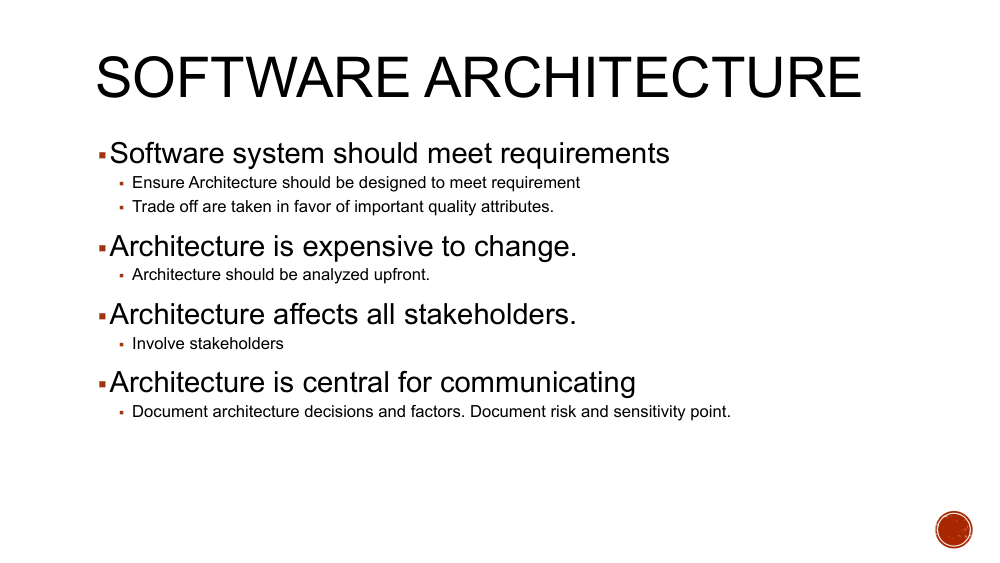
Architecture establishes the structural decisions that shape how a system is built, deployed, operated, changed, and scaled. Those decisions include decomposition, communication patterns, data ownership, technology platforms, deployment topology, redundancy, integration mechanisms, and cross-cutting controls. Once many teams, APIs, schemas, operational processes, and customer experiences depend on those choices, changing them can become expensive.
ATAM therefore encourages analysis before implementation momentum turns an architectural assumption into a constraint. It also creates a shared language between architects and stakeholders. Rather than debating broad statements such as “the system must be scalable,” teams define scenarios precise enough to analyze: scalable for what workload, at what growth rate, under what response-time expectation, with what operational constraints?
Quality attributes connect architecture to stakeholder needs
A quality attribute describes how well a system performs some aspect of its behavior or operation. ATAM uses quality attributes because functional requirements alone do not explain whether an architecture can support the conditions under which the system must succeed.
From vague qualities to analyzable scenarios
A useful ATAM discussion moves from broad attributes to scenarios. “High availability” is too vague to evaluate. A scenario can specify a stimulus, environment, affected artifact, expected response, and a measurable or observable response target. For example: “If one application instance fails during peak traffic, requests are automatically routed to healthy instances and the service remains available without losing committed transactions.”
This scenario format forces a team to connect architecture mechanisms: such as redundancy, health checks, idempotency, state management, and recovery behavior: to a concrete stakeholder expectation.
The core ATAM concepts: risks, sensitivity points, and tradeoff points
| Concept | Meaning | Example |
|---|---|---|
| Risk | An architectural decision or uncertainty that may prevent an important quality goal from being achieved. | A single shared database becomes a throughput bottleneck for projected traffic growth. |
| Non-risk | An architectural decision that analysis indicates is acceptable under the documented assumptions. | Horizontal scaling meets expected load because application nodes are stateless and load tests validate the target envelope. |
| Sensitivity point | A property where a small change can have a significant effect on a quality attribute. | Timeout configuration strongly affects both perceived latency and failure behavior. |
| Tradeoff point | A decision that affects more than one quality attribute, often in different directions. | Stronger synchronous consistency improves correctness expectations but can reduce availability or increase latency during network partitions. |
| Risk theme | A pattern that groups several individual risks around a broader threat to business or system goals. | Multiple risks trace back to insufficient isolation between tenants, threatening enterprise adoption. |
The ATAM process: from business drivers to architectural findings
The SEI describes ATAM as a stakeholder-centered evaluation that connects business goals, architectural approaches, and quality-attribute scenarios. The widely used ATAM flow includes nine steps:
- Present the ATAM. Explain the method, participants, expectations, and outputs.
- Present business drivers. Clarify the system’s business goals, constraints, major stakeholders, and architectural priorities.
- Present the architecture. Describe the architecture at a level that makes the important decisions and dependencies visible.
- Identify architectural approaches. Record the major patterns, technologies, structures, and decision strategies being used.
- Generate the quality-attribute utility tree. Decompose important quality attributes into concrete scenarios and prioritize them.
- Analyze architectural approaches. Examine how the architecture addresses high-priority scenarios and identify risks, sensitivity points, and tradeoffs.
- Brainstorm and prioritize scenarios. Bring in the broader stakeholder group to surface additional concerns and prioritize them.
- Analyze architectural approaches again. Use the prioritized stakeholder scenarios as test cases against the architecture.
- Present results. Summarize scenarios, architectural approaches, risks, non-risks, sensitivity points, tradeoffs, and risk themes.
What is a utility tree?
The utility tree is a prioritization structure that turns business-important qualities into analyzable scenarios. At the top is overall system utility. Below that are quality attributes such as performance, availability, security, modifiability, and usability. These are refined into scenarios, which stakeholders then prioritize by business importance and architectural difficulty or risk. The result gives the evaluation team a disciplined way to focus analysis where it matters most.
Illustrative example: evaluating an online transaction platform
Suppose a transaction platform must support a tenfold traffic increase, maintain rapid response during peak demand, protect sensitive data, and allow weekly feature releases. The proposed architecture uses synchronous service-to-service calls, a shared relational database, centralized authentication, and multiple independently deployed services.
An ATAM session could surface several high-priority scenarios: a traffic spike, an identity provider slowdown, a database failover, deployment of a schema change, and a request to add a new product workflow. Each scenario is mapped to architectural decisions and quality goals.
The team might identify the shared database as a sensitivity point for scalability, because changes in connection limits, transaction duration, or write volume significantly affect throughput. Synchronous authorization on every request might become a tradeoff point: it improves centralized policy enforcement but can increase latency and broaden the blast radius of an identity-service outage. A tightly coupled database schema could become a risk to deployment independence and time to market.
The value is not that ATAM automatically chooses the “correct” architecture. The value is that the assumptions and consequences become explicit, prioritized, and testable. The team can then decide whether to redesign, prototype, benchmark, add redundancy, change integration patterns, or consciously accept a risk.
ATAM benefits: and what teams gain beyond the report
The visible output of an ATAM evaluation is a set of findings. The larger benefit is often organizational: architects explain why decisions were made, business stakeholders clarify what they actually value, engineers expose operational realities, and quality goals become specific enough to drive further tests and design work.
Limitations to remember
ATAM depends on the quality of the architecture description, stakeholder participation, scenarios, assumptions, and facilitation. It is not a replacement for load testing, resilience testing, security reviews, cost modeling, reliability engineering, or detailed design verification. Instead, it helps decide where those deeper analyses should be concentrated.
How to use ATAM effectively in modern architecture reviews
For a practical architecture review, begin with a small set of the most important business drivers and quality attributes, then turn them into concrete scenarios. Avoid evaluating every possible quality at the same depth. Prioritize. Capture assumptions. Record which architectural decisions influence each scenario and where the evidence is strong, weak, or missing.
Finally, connect each significant risk to a next action: an architecture change, prototype, benchmark, failure-injection test, threat-modeling exercise, dependency review, cost experiment, or explicit risk acceptance. In this way, ATAM becomes not just a workshop but a bridge from architecture discussion to engineering evidence.
Architecture evaluation Quality attributes Risk analysis Tradeoff analysis Utility tree
Frequently asked questions
What is ATAM?
The Architecture Tradeoff Analysis Method is a structured method for evaluating a software architecture against important quality-attribute goals and identifying architectural risks, sensitivity points, and tradeoffs.
What does ATAM produce?
Typical outputs include prioritized quality-attribute scenarios, a utility tree, documented architectural approaches, risks and non-risks, sensitivity points, tradeoff points, and broader risk themes.
When should ATAM be used?
ATAM is especially useful when major architectural decisions have been proposed but there is still time to change them before implementation, integration, and operational dependencies make changes more expensive.
Is ATAM a performance test or security audit?
No. ATAM can expose performance, security, availability, modifiability, and other architectural risks, but it does not replace detailed testing, modeling, threat analysis, or operational validation.
Sources and further reading
This article expands the supplied ATAM slides and uses authoritative Software Engineering Institute material for the method description and process. See SEI’s Architecture Tradeoff Analysis Method collection, The Architecture Tradeoff Analysis Method, and Steps in an Architecture Tradeoff Analysis Method: Quality Attribute Models and Analysis.